
13 Must-have Tools for Your Android Pentesting (Updated for 2026)



Key Takeaways
- LSPatch brings Xposed modules to non-rooted Android devices.
- FridaLoader auto-downloads and launches the right Frida server for the device architecture.
- Applist Detector and Momo show which root or client-side detection checks are still failing.
- Shamiko and HideMyList hide root status and installed apps to get past root detection.
- Movecert moves certificates from the user store to the system store for traffic interception.
- Android Proxy Toggle switches the device proxy on and off from a quick settings tile.
- AAB Installer and SAI install .aab bundles and split APKs that standard installers can't handle.
Introduction
In today’s digital age, cybersecurity has become a significant concern for individuals and organizations alike. As mobile devices continue to grow in popularity, it’s important to ensure they are secure and protected from potential cyber-attacks. One way to do this is through penetration testing or “pentesting.” Pentesting involves simulating a real-world attack on a system or network to identify vulnerabilities and weaknesses that can be exploited by attackers.
This article will discuss 13 must-have Android pentesting tools that every security-conscious individual or organization should have in their toolkit. With these tools, you can rest assured that your Android device is protected against any malicious activity.
1. LSPatch
LSPatch is a rootless implementation of LSPosed Framework, it allows you to install Xposed modules on a non-rooted Android device. Modules that do not require root access will work with this.
2. FridaLoader
FridaLoader is a lazy way to quickly download and launch the latest version of Frida Server on any Emulator or device. This application automatically downloads the latest Frida server on your device based on its architecture. All you need to do is install the application and give it super user access.
3. Applist Detector
Applist Detector is an application that helps check what specific checks are failing when you are trying to bypass root detection/any other client-side detection during a pentest. If your target application refuses to work, you can check the applist detector to see if anything specific is being detected, it helps you narrow down what bypasses you need to apply to go forward/if the current bypasses are working properly or not.
4. Momo
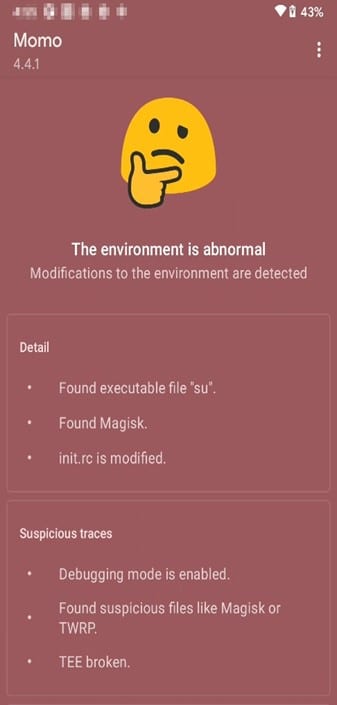
Momo is a detection application that reveals the specific checks that are failing on a physical testing device. When you have exhausted all attempts to bypass restrictions and the application still refuses to run, this proof-of-concept app comes to the rescue. It proves valuable when you are unable to identify the particular check that you may have overlooked or failed to bypass. The POC is attached. The device on the left is a rooted testing device, and the right is nonrooted but running on a custom ROM.
https://github.com/canyie/Riru-MomoHider
5. Android Proxy Toggle
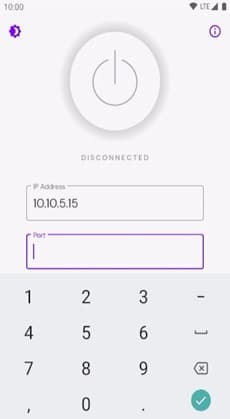
Wasting time turning proxy on and off from Wi-Fi Settings during a pentest? Here is Proxy Toggle for Android, which can help avoid that. You have to configure it once and then use a quick setting tile to toggle the proxy on and off.
https://github.com/theappbusiness/android-proxy-toggle
6. Movecert
Movecert moves certificates from the user certificate store to the system store. Removing the Network may also be a monitored warning.
https://github.com/Magisk-Modules-Repo/movecert
7. Shamiko
The Shamiko Magisk module offers a range of exciting features to enhance the functionality of your rooted Android device. Some of the key features of this module include the ability to hide your device’s root status, bypass SafetyNet checks, and access banking apps that were previously unavailable.
https://github.com/LSPosed/LSPosed.github.io/releases
8. AAB Installer
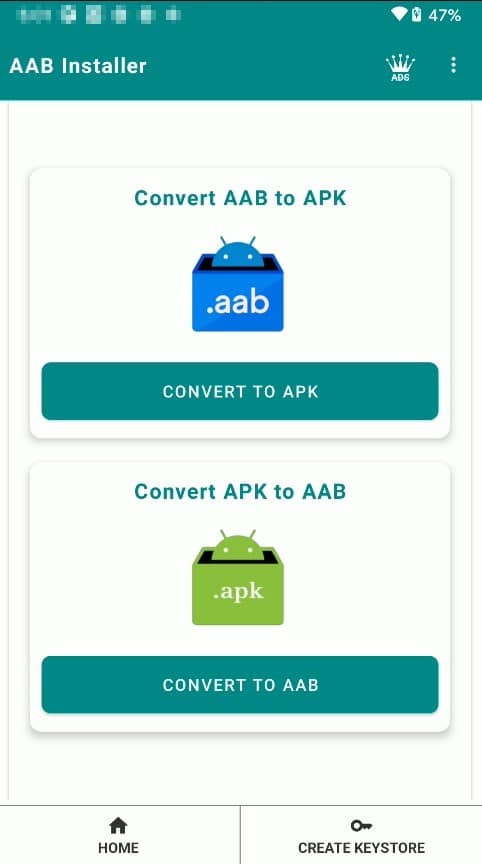
AAB Installer allows you to convert ‘.aab’ file to ‘.apk’ file and ‘.apk’ file to ‘.aab’ file. This app allows the installation of AAB files on Android devices. This application does not edit or change the AAB or APK file. It provides a platform where you can install an AAB file. This is necessary for developers because sometimes a sign may contain some error. So, this application is helpful for developers because they can easily convert their AAB to APK and APK to AAB. AAB installer also provides the feature to sign the app with a test key or custom Keystore.
https://play.google.com/store/apps/details?id=com.shapun.aabinstaller&hl=en&gl=US
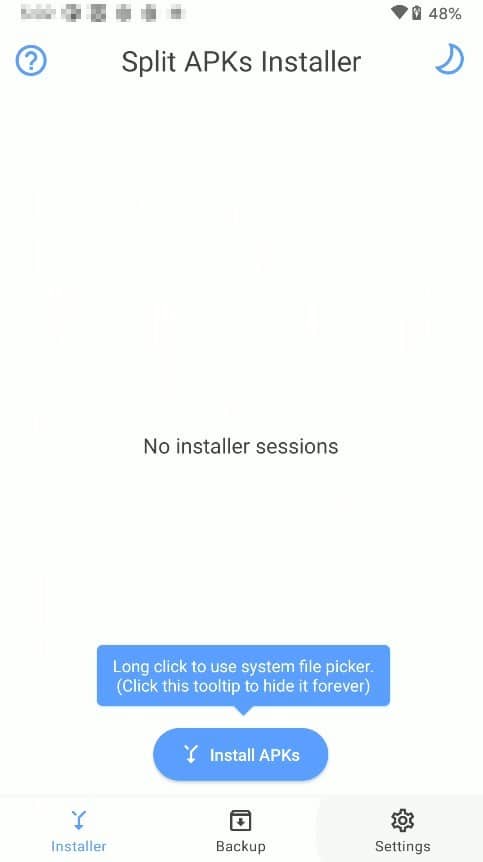
9. Split APKs Installer SAI
This is an installer for Split APKs.
https://play.google.com/store/apps/details?id=com.aefyr.sai
10. Shizuku
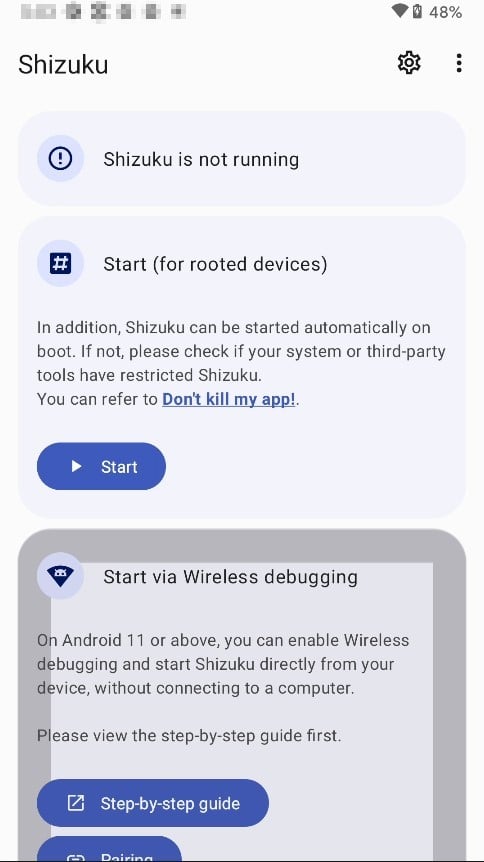
Shizuku can help normal apps use system APIs directly with adb/root privileges with a Java process started with app_process.
https://play.google.com/store/apps/details?id=moe.shizuku.privileged.api&hl=en_IN
11. LibChecker – Shizuku
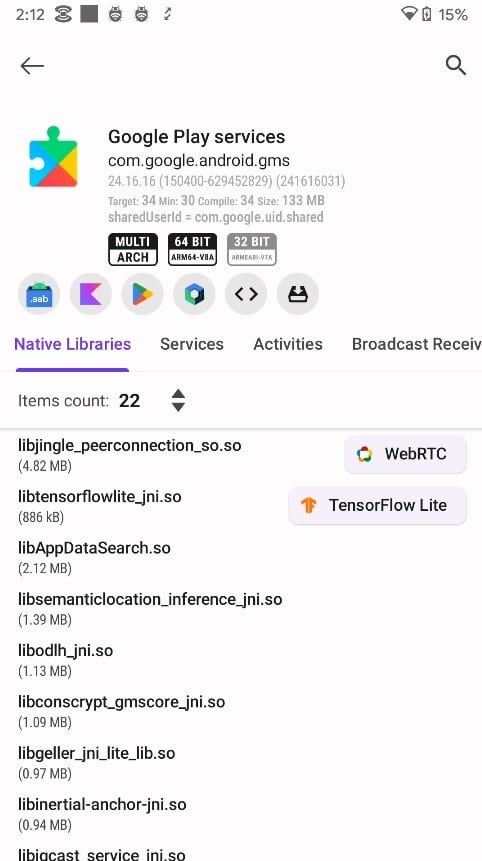
This app views the third-party libraries used by applications on your device. It can view the ABI architecture of the application’s native library (in general, whether the application is 64-bit or 32-bit). It can also view well-known libraries marked by The Rule Repository and can even sort and view them according to the number of library references.
https://github.com/LibChecker/LibChecker
12. Island
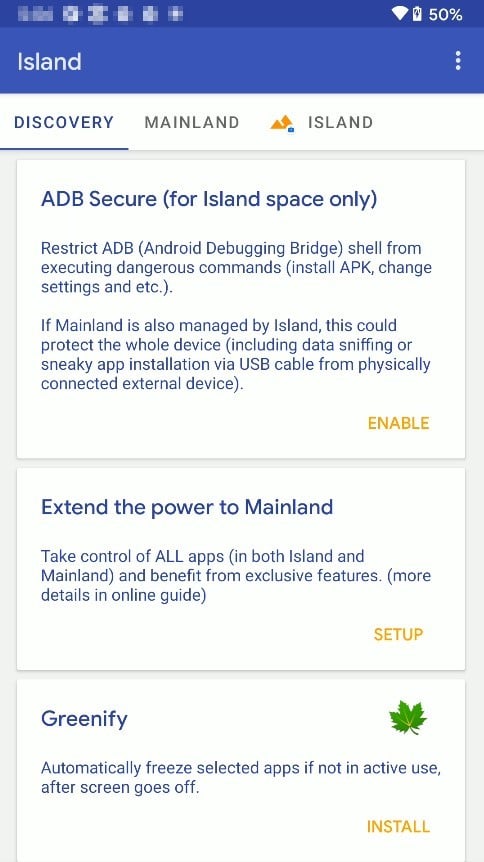
Island is an application that creates a sandboxed environment inside a device.
https://play.google.com/store/apps/details?id=com.oasisfeng.island
13. HideMyList
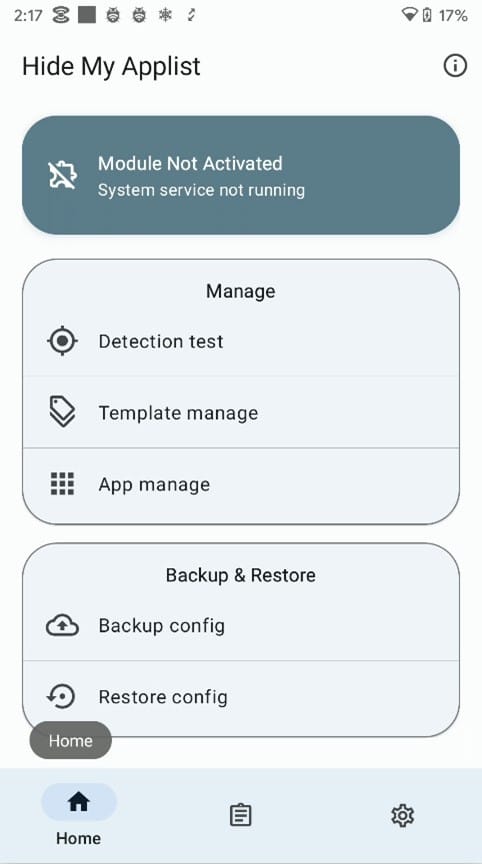
Although it’s bad practice to detect the installation of specific apps, not every app using root supports random package names. In this case, if root-related apps (such as Fake Location and Storage Isolation) are detected, it is tantamount to detecting that the device is rooted. Additionally, some apps use various loopholes to acquire your app list, to use it as fingerprinting data or for other nefarious purposes. This module can work as an Xposed module to hide apps or reject app list requests and provide some methods to test whether you have hidden your app list properly.
https://github.com/Dr-TSNG/Hide-My-Applist

Keep Reading





We break browsers before someone else does
This is the default text value

