
Get paid to find the bugs
150+


10+
Flexible
150+
10+
Flexible
Open roles, right now.
Cloud Security Consultant
Own the cloud security posture of a live AWS environment. This is a build-and-operate role covering CSPM, preventive guardrails, threat detection, and EKS security, not an advisory seat.


Cloud Security Consultant
Payatu is a research-powered cybersecurity services company specializing in penetration testing across web applications, mobile apps, cloud, and thick clients. We focus on finding business logic flaws and application-specific issues that automated scanners walk right past.
Payatu, an ISO-certified company, is dedicated to creating a safer digital world. We are a service-based cybersecurity company focused on deep, research-driven security testing across web, mobile, cloud, and thick client environments.
What we look for outside work parameters?
- Your expertise is your primary qualification, not your degree or certification
- Public work counts as credentials: papers, tools, write-ups, CTF results, exploit publications, and Hall of Fame listings
- Conference papers and presentations are valued
- Active participation in and contribution to the security community
- Certifications such as OSCP, CREST, and OSWE are a plus but not required
- AI security skills are a bonus, whether attacking AI systems or building automation for testing
About the role:
This is a build-and-operate role, not advisory. You will own the security posture of Angel One Wealth’s AWS environment, covering Cloud Security Posture Management (CSPM), preventive guardrails that stop risky changes before production, cloud threat detection and response via XDR, and securing Amazon EKS workloads.
What you will do:
- Deploy, tune, and operate a CSPM tool (AWS Security Hub, Wiz, or Prisma Cloud) across all AWS accounts
- Monitor continuously for misconfigurations, configuration drift, and non-compliant resources
- Triage findings and work with application and infrastructure owners until resolution
- Map controls to internal policy and SEBI CSCRF requirements
- Build preventive controls using SCPs, AWS Config rules, IAM permission boundaries, and guardrails-as-code
- Block or auto-remediate non-compliant resources at creation time
- Create automated remediation playbooks for common issues such as open security groups, public S3 buckets, unencrypted storage, and overly permissive IAM roles
- Coordinate with the CrowdStrike team on coverage and policy, and with the SOC to ensure logs reach the SIEM
- Harden Kubernetes clusters per CIS Benchmarks: pod security standards, admission controls, and network policies
- Enforce image scanning and signing in CI/CD pipelines, with proper secrets management
- Provide runtime threat detection for containers
- Review infrastructure-as-code (Terraform/CloudFormation) with DevOps and platform teams
- Maintain audit-ready evidence for VAPT, cyber audits, and regulatory reviews
- Join an on-call rotation for critical cloud security incidents
What we are looking for:
- 3-6 years in cloud security or DevSecOps, with at least 2 years focused on AWS
- Production experience with a CSPM tool (Security Hub/Config, Wiz, Prisma Cloud, Orca, or similar)
- Experience writing and enforcing AWS guardrails: SCPs, Config rules, IAM policy design, and/or policy-as-code (OPA/Rego, Sentinel)
- Experience operating an XDR platform (CrowdStrike, SentinelOne, Microsoft Defender, or Cortex XDR), including tuning and response
- Working knowledge of EKS security: RBAC, network policies, pod security, and image scanning
- Strong understanding of IAM, VPC networking, KMS encryption, and logging (CloudTrail, VPC Flow Logs, GuardDuty)
- Proficiency with Terraform and/or CloudFormation, and scripting in Python or Bash
Good to have:
- AWS Certified Security - Specialty
- Certified Kubernetes Security Specialist (CKS)
- Experience in a SEBI-regulated or other regulated financial services environment
- Familiarity with SEBI’s Cybersecurity and Cyber Resilience Framework (CSCRF)

Cloud Security Consultant - Delhi
Secure cloud environments, harden CI/CD pipelines, and drive security findings to closure. We want hands-on practitioners who build security into development workflows, not just report on it.
Cloud Security Consultant - Delhi
Payatu is a research-powered cybersecurity services company specializing in penetration testing across web applications, mobile apps, cloud, and thick clients. We focus on finding business logic flaws and application-specific issues that automated scanners miss.
Payatu, an ISO-certified company, is dedicated to creating a safer digital world. We are a service-based cybersecurity company focused on deep, research-driven security testing across web, mobile, cloud, and thick client environments.
What we look for outside work parameters?
- Your expertise is your primary qualification, not your degree or certification
- Published papers, tools, exploits, CTF results, Hall of Fame listings, or conference talks
- Community contributions to the security ecosystem
- Cloud, DevSecOps, and container security certifications are a plus
- AI security skills earn bonus points
What you will do:
- Deploy, tune, and operate CSPM/CNAPP tools (e.g., Wiz, Prisma Cloud, AWS Security Hub) across cloud environments
- Monitor for misconfigurations, excessive permissions, drift, and attack paths
- Triage and validate alerts, reduce false positives, and coordinate fixes with engineering teams
- Investigate exposed credentials and guide revocation, rotation, vault migration, and Git history cleanup
- Improve secrets detection logic and repository hygiene practices
- Assess and harden CI/CD pipelines, including secrets handling, branch protection, approval gates, and environment isolation
- Integrate code, dependency, IaC, and container scanning into pipelines (Jenkins, GitHub Actions, GitLab CI/CD, Azure DevOps)
- Review Terraform, CloudFormation, and other IaC for misconfigurations; apply least-privilege IAM and secure cloud networking
- Automate triage, remediation, and reporting with Python, Bash, PowerShell, or similar
- Track SLAs and ageing findings, escalate overdue issues, and verify closure
- Build dashboards and reports on finding volumes, remediation rates, and trends
- Write runbooks, playbooks, SOPs, and knowledge-base articles
- Work with cloud, DevOps, and architecture teams to fix gaps and identify recurring issues
What we are looking for:
- 3-6 years in cloud security operations, DevSecOps, CI/CD security, or a closely related security engineering role
- Hands-on cloud security experience, preferably AWS (Azure or GCP also considered)
- Experience operating and tuning CSPM/CNAPP tools to prioritize and remediate risk
- Ability to translate findings into actionable guidance for engineering and DevOps teams
- Ownership mindset across the full finding lifecycle, including SLA tracking and escalation
Good to have:
- Cloud, DevSecOps, or container security certifications
- Experience with scanners such as Checkov, tfsec, Trivy, Semgrep, or Snyk
- Policy-as-code and detection-as-code familiarity
- ITSM or ticketing platform experience for finding lifecycle management
- Enterprise or globally distributed environment experience
- Agile or sprint-based delivery experience
- Support for compliance audits, evidence collection, and remediation reporting
Finance Manager
Join our Bandit team and power the finance engine behind a safer digital world. We are looking for people who love innovation, ownership, and teamwork.
Finance Manager
Payatu, an ISO-certified company, is dedicated to creating a safer digital world. Our team brings together a passion for growth, learning, and collaboration across operations, IT, finance, HR, and sales/marketing, with plenty of opportunities to make a difference and grow your career.
Payatu, an ISO-certified company, is dedicated to creating a safer digital world. Our team brings together a passion for growth, learning, and collaboration across many fields. Whether you’re in operations, IT, finance, HR, or sales/marketing, you’ll find plenty of opportunities to make a difference and grow your career with us.
**What we look for outside work parameters? **
- Your expertise is your primary qualification, not your degree or certification.
- Strong leadership qualities, plan, monitor and manage activities for self and team.
- Passion to deliver the promised service.
- Motivated, self-starter individual with high level of integrity, intensity, and activity with a can-do attitude.
- Ability to understand Organization objectives and execute them accordingly.
- Disciplined process-oriented work style and ability to work independently
What you will do:
- Record, verify, consolidate, and enter transactions to keep accounting data accurate
- Manage accounts receivable and payable, including payment follow-ups with sales teams and customers
- Vouch vendor invoices in Tally Prime
- Handle monthly TDS, GST, professional tax, and PF payments
- Run the end-to-end payroll process
- Prepare entries for assets, liabilities, revenue, and expenses
- Maintain subsidiary accounts and the general ledger, including trial balances and reconciliations
- Prepare balance sheets, P&L statements, and other financial reports on schedule
- Complete monthly and quarterly account reconciliations
- Review intercompany transactions and generate invoices as needed
- Stay current on legal and compliance requirements
- Perform database backups to protect financial information
What we are looking for:
- Bachelor’s or master’s degree in accounting, finance, or a related field, with strong MS Excel skills
- 5+ years of experience in general and tax accounting or finance
- Working knowledge of Tally Prime, TDS, and GST returns, plus bank reconciliation
- Expert knowledge of GAAP and Ind AS; proficiency in Tally Prime, Zoho Books, Excel, PowerPoint, and Power BI
- Experience implementing financial MIS solutions and driving process improvements
- Ability to handle complex transactions and multiple priorities
- Strong communication skills, including explaining financial topics to non-technical stakeholders
Secure Code Review Consultant
Are you interested in automating the build and deployment process of the application with ensuring the application security?
Secure Code Review Consultant
Are you interested in automating the build and deployment process of the application with ensuring the application security? If yes, then Payatu is the place for you. We are always in search of passionate people to expand our renowned Bandit family at Payatu. In the quest for Bandits, here is an excellent opportunity we would like to share with you.
Payatu is a GPTW certified company where we strive to create a culture of excellence, growth and innovation that empowers our employees to reach new heights in their careers. We are young and passionate folks driven by the power of the latest and innovative technologies in IoT, AI/ML, Blockchain, and many other advanced technologies. We are on the mission of making Cyberworld safe for every organization, product, and individual.
What we look for outside work parameters?
- Your expertise is your primary qualification, not your degree or certification.
- Your publicly known contributions are your credentials.
- Papers you have written, tools you have developed are your references.
- Your write-up reflects your interests and ethics.
- Your published exploits, your CTF scores, and hall of fame listings are the testimonies of your work.
- Your research paper was published and presented at conferences.
- You are learning from the community and enthusiastically contributing back.
You are a perfect technical fit if you have:
- Strong fundamental of application and network protocols.
- Strong hold on Web application security concept and penetration testing skill.
- Good command of at least one programming language.
- Good understanding of basic coding and core concepts to understand the flow of code.
- Good understanding of OWASP Top 10 and other web-related vulnerabilities as well as logic flaws.
- Hands-on experience in performing penetration testing of web-based applications preferably in the financial domain.
- Good to have experience in working alongside the development/QA teams.
- Good report writing and presentation skills.
- Should be able to suggest optimum security improvements to application components.
You Have All Our Desired Qualities, if:
- You have experience in web application and web service security assessment.
- You have a history of publishing or presenting good research.
- You have the knack of finding security bugs in everything you touch.
- You like automating stuff.
- You like writing tools.
- You have excellent written and verbal communication skills and the ability to express your thoughts clearly.
- You have the skill to articulate and present technical things in business language.
- You can work independently as well as within a team and meet project schedules and deadlines.
- You have strong problem solving, troubleshooting, and analysis skills.
- You are passionate about your area of expertise and self-driven.
- You are comfortable working in a dynamic and fast-paced work environment.
- You are Self-driven, proactive, hardworking, team-player.
- You are working on something on your own in your field apart from official work.
Your everyday work will look like:
- Security assessment of web application and web service on various platforms.
- Back your findings with Proof-of-concept exploits.
- Collect evidence and maintain a detailed write-up of the findings.
- Understand and explain the results with impact on business and compliance status.
- Explain and demonstrate vulnerabilities to application/system owners.
- Provide appropriate remediation and mitigations of the identified vulnerabilities.
- Individually or collaboratively review the system designs, source code, configurations, communications for security gaps.
- Deliver results within stipulated timelines.
- Sharpen your saw with continuous research, learning, training on the latest tools and techniques, keeping up with new research, and sharing the same with the ecosystem.
- Communicate well using verbal and written skills, within and out of the team.
Red Team Security Consultant
Are you interested in automating the build and deployment process of the application while ensuring application security?
Red Team Security Consultant
(Junior to Senior — broad experience band)
Are you interested in automating the build and deployment process of the application while ensuring application security? If yes, then Payatu is the place for you. We are always in search of passionate people to expand our renowned Bandit family at Payatu. In the quest for Bandits, here is an excellent opportunity we would like to share with you.
Payatu is a GPTW certified company where we strive to create a culture of excellence, growth and innovation that empowers our employees to reach new heights in their careers. We are young and passionate folks driven by the power of the latest and innovative technologies in IoT, AI/ML, Blockchain, and many other advanced technologies. We are on the mission of making the Cyberworld safe for every organization, product, and individual.
What we look for outside work parameters:
- Your expertise is your primary qualification, not your degree or certification.
- Your publicly known contributions are your credentials.
- Papers you have written, tools you have developed are your references.
- Your write-up reflects your interests and ethics.
- Your published exploits, CTF rankings, and Hall of Fame listings are testimonies of your work.
- Original tools or scripts you've open-sourced count in your favor.
- Your research paper was published and/or presented at a conference.
- You are learning from the community and enthusiastically contributing back.
You are a perfect technical fit if
- Strong fundamentals of application, network, and Windows/Active Directory protocols.
- Design and execute advanced penetration testing, vulnerability assessments, and simulated attack scenarios (Red Team, Purple Team) to identify security weaknesses across an organization's systems, networks, cloud, and applications.
- Utilize a variety of tools and techniques to develop and implement sophisticated attack strategies, mimicking the tactics, techniques, and procedures used by real-world adversaries.
- Collaborate with the Blue Team to test and enhance incident response capabilities through Red vs. Blue exercises and Purple Team workshops, identifying gaps and recommending detection/mitigation improvements.
- Document and communicate detailed findings — vulnerabilities, exploit chains, and remediation guidance — in clear, actionable reports for technical and executive stakeholders.
- Stay current with emerging threats and attack vectors; develop or customize tools, scripts, and techniques to enhance Red Team capabilities.
- Strong planning and execution of social engineering attacks — phishing, vishing, pretexting, baiting, and tailgating — to assess human vulnerabilities and insider-threat risk.
- Solid grounding in web application security with hands-on pentesting experience, preferably including regulated or financial-domain applications.
- Good command of at least one programming/scripting language for tooling and automation.
- Should be able to suggest optimum security improvements to application and infrastructure components.
You Have All Our Desired Qualities, if
- Hands-on Active Directory exploitation and lateral movement experience, including credential attacks, privilege escalation, and abuse of trust relationships.
- Comfortable with attack-path mapping tools and holds a recognized AD-focused certification.
- Offensive experience across major cloud and identity platforms, including privilege escalation, token/credential abuse, and misconfiguration exploitation.
- Ability to assess cloud landing zones and enterprise perimeter/identity infrastructure end-to-end.
- Named, hands-on experience with command-and-control frameworks — not just conceptual familiarity.
- Practical defense-evasion skills against modern endpoint protection and detection controls.
- Understanding of C2 infrastructure design and operational security practices.
- Experience threat-modeling and adversarially testing AI/LLM-powered applications and agentic systems.
- Exposure to building or red-teaming AI-augmented offensive tooling or automation pipelines.
- Deep web and API security expertise, including chained and business-logic vulnerabilities.
- Track record of vulnerability discovery and/or public bug bounty program participation.
- Comfortable with large-scale reconnaissance, source/asset analysis, and secrets exposure hunting.
- Experience running or supporting Purple Team exercises that translate red findings into detection improvements.
- Threat hunting fundamentals, including log/telemetry analysis and familiarity with detection/monitoring platforms.
- Security assessment experience with CI/CD pipelines and build/release infrastructure.
- Container and orchestration security experience.
- You like automating stuff and writing your own tools to scale assessments.
- Experience with distributed or large-scale scanning infrastructure is a strong plus.
- Excellent written and verbal communication; able to translate technical impact into business/compliance language for non-technical stakeholders.
- Comfortable quantifying impact rather than describing findings only qualitatively.
- Can work independently and within a team, meet deadlines in a dynamic, fast-paced environment, and is self-driven, proactive, and hardworking.
- Actively working on something in the field outside of official work.
Your everyday work will look like
- Security assessment of web applications, APIs, networks, Active Directory, and cloud environments across various platforms.
- Design and execution of full-scope red team engagements — initial access through internal compromise to objective completion.
- Back your findings with working proof-of-concept exploits and reproducible attack chains.
- Collect evidence and maintain a detailed write-up of findings, mapped to relevant industry frameworks.
- Understand and explain results in terms of business and compliance impact.
- Explain and demonstrate vulnerabilities to application/system owners; run purple-team sessions with Blue Team counterparts.
- Provide appropriate remediation and mitigation guidance for identified vulnerabilities.
- Individually or collaboratively review system designs, source code, pipeline configurations, and communications for security gaps.
- Deliver results within stipulated timelines.
- Sharpen your saw with continuous research, learning, and training on the latest tools and techniques; share the same with the ecosystem.
- Communicate well using verbal and written skills, within and outside the team.
IoT Firmware Security Consultant
Is Firmware IOT Security that excites you the most? We are looking for cyber experts who will find vulnerability in IoT device firmware.
IoT Firmware Security Consultant
Is Firmware IOT Security that excites you the most? Do you have a strong understanding of embedded firmware security, coupled with hands-on of firmware reversing for ARM and X86 for OS based and BareMetal firmware? We are looking for cyber experts who will be a part of our ever growing IoT security ecosystem and find vulnerability in IoT device firmware. If you are a tech savant, apply now to become a part of this tech-powered and tech-inspired environment.
Payatu is the go-to cybersecurity consulting company that candidates have been turning towards to get the upper hand in their careers. You can have the same for yourself. If you are a tech savant, apply now to become a part of this tech-powered and tech-inspired environment.
Payatu is an ISO certified company where we strive to create a culture of excellence, growth and innovation that empowers our employees to reach new heights in their careers. We are a bunch of young and passionate folks who are driven by the power of the latest and innovative technologies in IoT, AI/ML, Blockchain, and many other advanced technologies. We are in the mission of making the Cyberworld safe for every organization, product, and individual.
You are a perfect technical fit if:
- You have strong understanding on Embedded firmware security.
- You have deep understanding and hands on with doing firmware reversing for ARM, MIPS and x86 for(either of it) OS based and BareMetal firmware.
- You have very good understanding of ARM and x86 architecture assembly language.
- You have deep concepts of Linux internals.
- You have understanding of Operating systems in detail.
- You have good knowledge of internal working of C programming.
- You must be good with at least one scripting language.
- You must have knowledge on embedded protocols such as UART, I2C, SPI, JTAG, SWD.
- You must have knowledge on Radio protocol internals such as BLE, WIFI.
What we look for outside work parameters?
- Your expertise is your primary qualification, not your degree or certification.
- Your publicly known contributions are your credentials.
- Papers/blogs you have written, tools you have developed are your references.
- You are learning from the community and enthusiastically contributing back.
You Have All Our Desired Qualities, if:
- You have the technical skills mentioned above.
- You have Passion for doing firmware reversing.
- You have a history of publishing or presenting good research.
- You have excellent written and verbal communication skills and ability to express your thoughts clearly.
- You can work independently as well as within a team and meet project schedule and deadlines.
- You are a creative individual to think out of the box for creating different firmware attacks on product.
Your everyday work will look like:
- Find vulnerability in IoT device firmware.
- Sharpen your saw with continuous research, learning, training on the latest tools and techniques, keeping up with new research and sharing the same with the ecosystem.
- Communicate well using verbal and written skills, within and out of the team.
Business Development Executive
Payatu is a leading cybersecurity services and research company known for delivering high-impact security assessments, innovative solutions, and valuable insights to enterprises worldwide.
Business Development Executive
Payatu is a leading cybersecurity services and research company known for delivering high-impact security assessments, innovative solutions, and valuable insights to enterprises worldwide. We value curiosity, collaboration, and the drive to make meaningful impact.
We are looking for a motivated Business Development Executive (BDE) to accelerate business growth by generating leads, building strong client relationships, and driving sales opportunities in our cybersecurity services portfolio. The ideal candidate will be proactive, target-driven, and experienced in consultative B2B sales.
Key Responsibilities
- Identify and qualify new business opportunities in target sectors and markets.
- Generate, nurture, and track leads through outbound outreach (calls, emails, LinkedIn).
- Build and maintain strong relationships with prospective clients and stakeholders.
- Conduct product/service presentations and tailored solution pitches.
- Meet and exceed individual sales targets and contribute to revenue growth.
- Work closely with delivery, marketing, and technical teams to ensure smooth proposals and conversions.
- Maintain accurate CRM records and prepare sales reports.
Qualifications
- Bachelor's degree in Business, Marketing, IT, or a related field.
- 2+ years of proven experience in B2B sales or business development (preferably in IT, tech, cybersecurity or SaaS).
- Strong communication, negotiation, and relationship-building skills.
- Comfortable with outbound prospecting, presentations, and closing deals.
- Experience with CRM tools and sales pipeline management.
- Ability to thrive in a fast-paced, target-driven environment.
What We Offer
- Competitive salary with performance-based incentives.
- Opportunity to work in a rapidly growing domain (cybersecurity).
- Professional growth and exposure to global clients.
Customer Success Manager
We are looking for a hungry, ambitious, and resourceful sales professional who wants to be an integral part of this challenging and fascinating journey.
Customer Success Manager
Don't Wish It Was Easier; Wish You Were Better. Don't Wish for Fewer Problems; Wish for More Skills. Don't Wish for Fewer Challenges; Wish for More Wisdom.
We are guided by these words of wisdom and looking for a hungry, ambitious, and resourceful sales professional who wants to be an integral part of this challenging and fascinating journey.
Payatu is an ISO certified company where we strive to create a culture of excellence, growth and innovation that empowers our employees to reach new heights in their careers. We are a bunch of young and passionate folks who are driven by the power of the latest and innovative technologies in IoT, AI/ML, Blockchain, and many other advanced technologies. We are in the mission of making Cyberworld safe for every organization, product, and individual.
Who are you?
You are a charismatic young creative hustler who loves to meet and engage with people. You straddle the gap between service and sales, between company interest and customer interest. You realize that business is more about helping a customer and solving their problem then only making a profit. You want to grow your career in the hyper growing cyber security industry.
You are a perfect fit for this if:
- You should have an experience in cyber security world.
- You have minimum of 2-4 years of experience in customer success, account management or related roles.
- You have demonstrated track record of managing customer relationships and driving customer satisfaction and retention.
- You are a team player who gels well in the team.
- You are a technology enthusiast and stay updated about new technology innovations.
- You have the tenacity to develop ideas independently and thrive in a fast-paced startup environment.
- You have the ability to apply significant knowledge of industry trends and developments to improve services to clients.
- You should have strong communication, negotiation, and presentation skills.
Your everyday work will look like:
- Learn about company product and service offerings.
- Incorporating strategies, themes, and other material into response sections.
- Proposal development, review and feedback incorporation based on various interactions with different stakeholders.
- Giving product demonstrations to prospects and answering their queries.
- You should have an excellent understanding of client's need and generating solutions of how our organization can provide that.
- Assisting clients through each step of the post-sales process, solution handling and helping them resolve any concerns or questions they may have while processing, tracking and completing sales efficiently.
- Develop a growth strategy focused both on financial gain and customer satisfaction.
- Build long-term relationships with new prospects and existing customers.
- Create contract-winning proposals for current and prospective clients.
- Attend weekly sales team meetings and provide information to management about sales figures, KPI, goals, and obstacles.
- Identifies trendsetter ideas by researching industry and related events, publications, and announcements.
- Update job knowledge by participating in educational opportunities, reading professional publications, maintaining personal network.
- Actively engage with customers to understand their goals, challenges, and key performance indicators (KPIs).
- Provide timely responses to customer inquiries, troubleshooting technical issues, and escalating when necessary.
- Conduct regular check-ins and account reviews with customers to assess satisfaction levels and identify areas for improvement.
- Collaborate with cross-functional teams to address customer feedback and drive product improvements.
IoT Radio Frequency Security Consultant
If you are someone who has the skills and the ability to design and conduct radio, IoT hardware attacks, then we are looking for you.
IoT Radio Frequency Security Consultant
If you are someone who has the skills and the ability to design and conduct radio, IoT hardware attacks, paired with the knowledge and expertise of hardware attacks such as PCB reversing, Component identification, Side channel attacks, memory extraction methods, then we are looking for you. Not all superheroes wear capes, but if you do wear the cape of embedded protocols such as UART, I2C, SPI, JTAG, SWD and possible attacks on them, then don't forget to reach out to us.
If you have knowledge of wireless communication, including expertise in radio protocols such as BLE and ZIGBEE, as well as familiarity with SDR and understanding of the associated attack surfaces pertaining to these wireless communication protocols, coupled with proficiency in MQTT and CoAP, along with knowledge on penetration testing of these protocols.
Payatu is a ISO certified company where we strive to create a culture of excellence, growth and innovation that empowers our employees to reach new heights in their careers. We are young and passionate folks driven by the power of the latest and innovative technologies in IoT, AI/ML, Blockchain, and many other advanced technologies. We are on the mission of making Cyberworld safe for every organization, product, and individual.
You are a perfect technical fit if:
- Strong understanding on Radio Protocol security.
- Familiar with the tools for the radio protocol assessment.
- Hands on with radio attacks on the BLE, ZIGBEE, SDR.
- Experience with Radio protocol attack such as BLE, WIFI, LoRa, DSP, SDR.
- Good to have knowledge on MQTT, CoAP and one programming language.
What we look for outside parameters:
- Your publicly known contributions are your credentials.
- Papers/blogs you have written, tools you have developed are your references.
- You are learning from the community and enthusiastically contributing back.
You Have All Our Desired Qualities, if:
- You have the technical skills mentioned above.
- You have Passion for attacking hardware.
- You have a history of publishing or presenting good research.
- You have excellent written and verbal communication skills and ability to express your thoughts clearly.
- You can work independently as well as within a team and meet project schedule and deadlines.
- You are a creative individual to think out of the box for creating different hardware attacks on product.
Your Everyday work will look like:
- Create radio attacks on existing IoT products and find vulnerability.
- Breaking the IoT product for finding security issues in radio protocols.
- Sharpen your saw with continuous research, learning, training on the latest tools and techniques, keeping up with new research and sharing the same with the ecosystem.
- Communicate well using verbal and written skills, within and out of the team.
IoT Hardware Security Consultant
If you are someone who has the skills and the ability to design and conduct radio, IoT hardware attacks, paired.
IoT Hardware Security Consultant
If you are someone who has the skills and the ability to design and conduct radio, IoT hardware attacks, paired with the knowledge and expertise of hardware attacks such as PCB reversing, Component identification, Side channel attacks, memory extraction methods, then we are looking for you. Not all superheroes wear capes, but if you do wear the cape of embedded protocols such as UART, I2C, SPI, JTAG, SWD and possible attacks on them, then don't forget to reach out to us. If you have knowledge of wireless communication, including expertise in radio protocols such as BLE and ZIGBEE, as well as familiarity with SDR and understanding of the associated attack surfaces pertaining to these wireless communication protocols, coupled with proficiency in MQTT and CoAP, along with knowledge on penetration testing of these protocols.
Payatu is a ISO certified company where we strive to create a culture of excellence, growth and innovation that empowers our employees to reach new heights in their careers. We are young and passionate folks driven by the power of the latest and innovative technologies in IoT, AI/ML, Blockchain, and many other advanced technologies. We are on the mission of making Cyberworld safe for every organization, product, and individual.
You are a perfect technical fit if you have:
- Strong understanding on Radio Protocol security.
- Familiar with the tools for the radio protocol assessment.
- Hands on with radio attacks on the BLE, ZIGBEE, SDR.
- Experience with Radio protocol attack such as BLE, WIFI, LoRa, DSP, SDR.
- Good to have knowledge on MQTT, CoAP and one programming language.
What we look for outside parameters:
- Your publicly known contributions are your credentials.
- Papers/blogs you have written, tools you have developed are your references.
- You are learning from the community and enthusiastically contributing back.
You have all our desired qualities, if:
- You have the technical skills mentioned above.
- You have Passion for attacking hardware.
- You have a history of publishing or presenting good research.
- You have excellent written and verbal communication skills and ability to express your thoughts clearly.
- You can work independently as well as within a team and meet project schedule and deadlines.
- You are a creative individual to think out of the box for creating different hardware attacks on product.
Your everyday work will look like:
- Create radio attacks on existing IoT products and find vulnerability.
- Breaking the IoT product for finding security issues in radio protocols.
- Sharpen your saw with continuous research, learning, training on the latest tools and techniques, keeping up with new research and sharing the same with the ecosystem.
- Communicate well using verbal and written skills, within and out of the team.
Application Security (AppSec) Consultant
Payatu is hiring an Application Security Consultant who's genuinely good at breaking things by hand, not someone who lets a scanner do the thinking.
Application Security (AppSec) Consultant
Payatu is hiring an Application Security Consultant who's genuinely good at breaking things by hand, not someone who lets a scanner do the thinking.
We are a service-based cybersecurity company, and pentesting is what we do all day, every day, across Web Apps, Mobile Apps, and Thick Clients. Our reputation is built on catching what automated scanners walk right past: business logic flaws and the application-specific bugs that only show up when someone sits down and thinks like an attacker instead of running through a checklist.
What we look for outside work parameters?
- Your expertise is your primary qualification, not your degree or certification.
- Your publicly known contributions are your credentials.
- Papers you have written, tools you have developed are your references.
- Your write-up reflects your interests and ethics.
- Your published exploits, your CTF scores, and hall of fame listings are the testimonies of your work.
- Your research paper was published and presented at conferences.
- You are learning from the community and enthusiastically contributing back.
- Certifications like OSCP, CREST, OSWE, and similar are a plus if you’ve got them, but we don’t gatekeep on degrees or certifications.
- Bonus points for AI security skills, on either side of the fence - attacking AI systems or building smart automation around your own testing.
You are a perfect technical fit if:
- 2-5 years of hands-on Web Application pentesting experience (mobile and thick client experience is a strong plus).
- Strong fundamental of application and network protocols.
- Strong hold on Web application security concept and penetration testing skill.
- Good command of at least one programming language.
- Good understanding of OWASP Top 10 and other web-related vulnerabilities as well as logic flaws.
- Hands-on experience in performing penetration testing of web-based applications preferably in the financial domain.
- Good to have experience in working alongside the development/QA teams.
- Good report writing and presentation skills.
- Should be able to suggest optimum security improvements to application components.
- Burp MCP is baked into our workflow, as part of your day-to-day testing.
- Source Code and Config Review experience is a plus for engagements that go beyond Black-Box.
- The instinct to poke at things until they break, and the patience to document exactly how.
You Have All Our Desired Qualities, if:
- You have experience in web application and web service security assessment.
- You have a history of publishing or presenting good research.
- You have the knack of finding security bugs in everything you touch.
- You like automating stuff.
- You like writing tools.
- You have excellent written and verbal communication skills and the ability to express your thoughts clearly.
- You have the skill to articulate and present technical things in business language.
- You can work independently as well as within a team and meet project schedules and deadlines.
- You have strong problem solving, troubleshooting, and analysis skills.
- You are passionate about your area of expertise and self-driven.
- You are comfortable working in a dynamic and fast-paced work environment.
- You are self-driven, proactive, hardworking, team-player.
- You are working on something on your own in your field apart from official work.
Your everyday work will look like:
- Manual penetration testing of Web Applications, Mobile Applications, and Thick Clients (automation is a starting point here, not the finish line).
- Finding the business logic flaws and app-specific bugs that only show up when a human actually tries to break the app.
- Security assessment of web application and web service on various platforms.
- Back your findings with Proof-of-concept exploits.
- Collect evidence and maintain a detailed write-up of the findings.
- Understand and explain the results with impact on business and compliance status.
- Explain and demonstrate vulnerabilities to application/system owners.
- Provide appropriate remediation and mitigations of the identified vulnerabilities.
- Individually or collaboratively review the system designs, source code, configurations, communications for security gaps.
- Deliver results within stipulated timelines.
- Sharpen your saw with continuous research, learning, training on the latest tools and techniques, keeping up with new research, and sharing the same with the ecosystem.
- Communicate well using verbal and written skills, within and out of the team.
- Reports detailed enough for a developer to fix it, clear enough for a stakeholder to get why it matters.
- Using automation and AI to work more efficiently, whether that means building tooling to speed up repetitive parts of testing or using AI to sharpen your workflow, all in service of delivering higher-quality work, not cutting corners on it.
- Roughly 30% of your time is set aside for research. You choose the topic, and it’s treated as a real part of the job, not something squeezed in on the side.
Don't see your role?
What being a Bandit gets you




Services, framed by your problem.
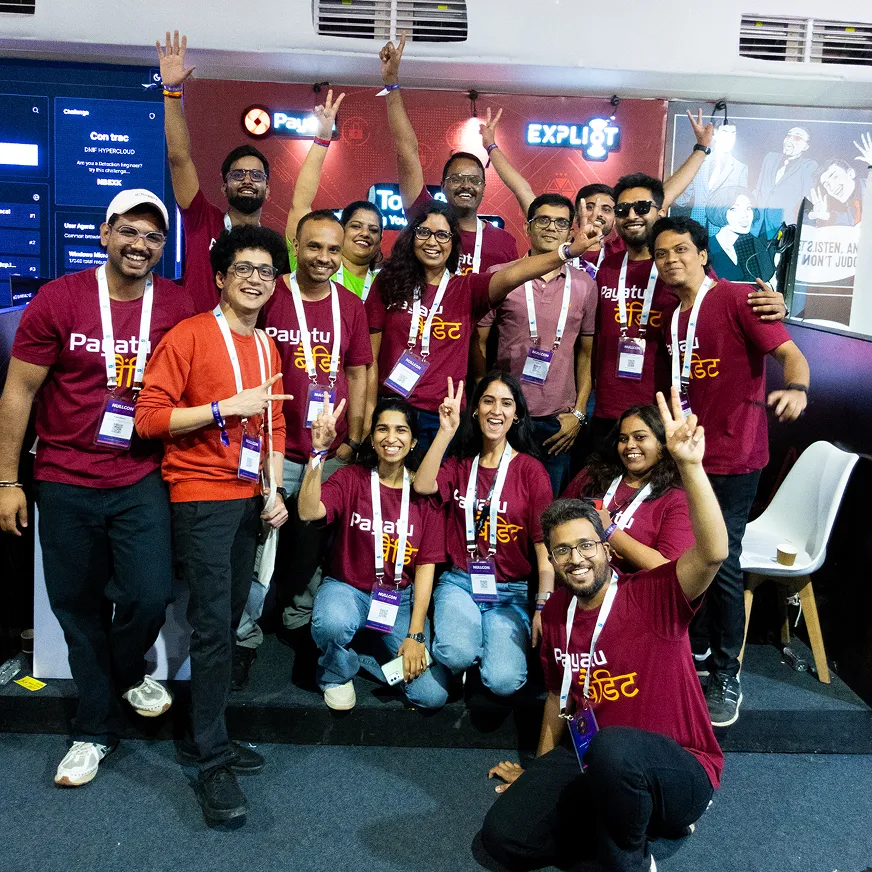
You would be working with the people who find the bugs

What to expect when you apply
Apply
Send your CV and anything that shows how you think CVEs, tools, writeups, CTF profiles.
Technical chat
A conversation with the team you'd join less quiz, more "how would you approach this?"
Practical task
A hands-on exercise close to real work, so you see us and we see you at your best.
Offer
A final chat on growth and fit, then an offer. Clear timelines throughout no ghosting.

Questions Web Application teams ask us.
Ready to be a Bandit?
Browse the open roles and apply or send us your best work and start a conversation.

